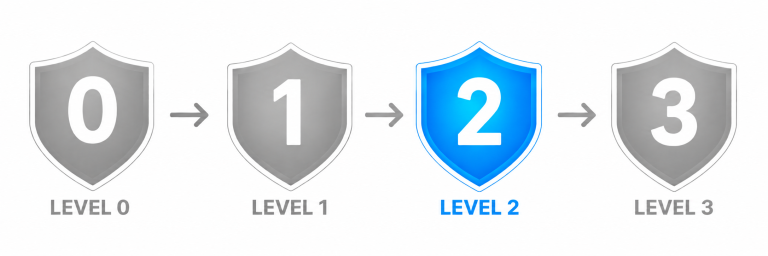
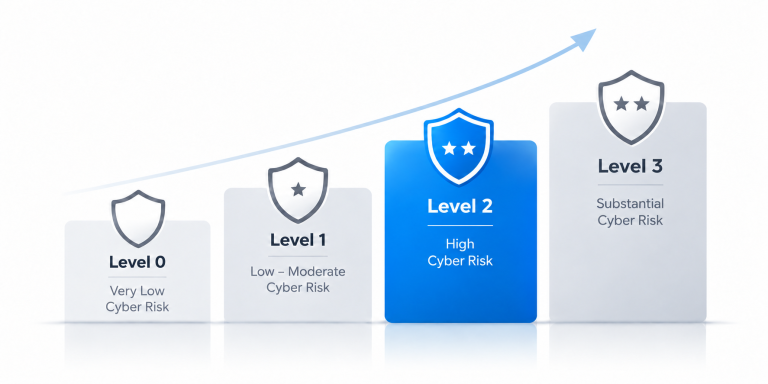
Designed for suppliers where there is a high level of assessed cyber risk, requiring advanced cyber security oversight, planning and robust organisational practices.
Advanced Defence Cyber Certification for suppliers operating at a high level of assessed cyber risk.
DCC Level 2 is designed for organisations operating at a high level of assessed cyber risk. It requires advanced cyber security oversight and planning, demonstrating that robust organisational, technical and operational security practices are embedded across the business. Assessment is undertaken against Def Stan 05-138 Issue 4 and covers 139 controls.
Key facts about DCC Level 2 and its advanced cyber security requirements.
139 Controls
DCC Level 2 assesses 139 controls across the organisation, requiring robust governance, technical security, resilience and cyber risk management practices.
Cyber Essentials Plus
A current Cyber Essentials Plus certification is required for DCC Level 2, providing independently verified assurance that key technical security controls are implemented effectively.
High Cyber Risk
DCC Level 2 is intended for organisations and contracts assessed as presenting a high level of cyber risk, requiring advanced cyber security oversight, planning and robust organisational practices.
Advanced Oversight
DCC Level 2 requires advanced cyber security oversight and planning, ensuring robust organisational and cyber security practices are implemented, managed and maintained across the organisation.
DCC Level 2 at a Glance
Key facts about DCC Level 2 and its advanced cyber security requirements.
139 Controls
Advanced Cyber Assurance
DCC Level 2 assesses 139 controls across the organisation, requiring robust governance, technical security, resilience and cyber risk management practices.
Advanced cyber security requirements
Cyber Essentials Plus
Verified Technical Security
A current Cyber Essentials Plus certification is required for DCC Level 2, providing independently verified assurance that key technical security controls are implemented effectively.
DCC Level 2 is intended for organisations and contracts assessed as presenting a high level of cyber risk, requiring advanced cyber security oversight, planning and robust organisational practices.
Designed for a high DCC Cyber Risk Profile
Advanced Oversight
Robust Security Governance
DCC Level 2 requires advanced cyber security oversight and planning, ensuring robust organisational and cyber security practices are implemented, managed and maintained across the organisation.
Driving robust organisational and cyber security practices
DCC Level 2 Certification from a Level 3 Certification Body
KEYSIGMA is an authorised DCC Level 3 Certification Body, qualified to independently assess and certify organisations across DCC Levels 0–3.
Authorised under the IASME Defence Cyber Certification scheme
DCC Level 2 assesses your organisation’s cyber security capability across four core objectives defined within Def Stan 05-138 Issue 4.
Across these objectives, organisations must demonstrate advanced cyber security oversight, planning and robust security practices appropriate to a high level of assessed cyber risk.
Managing Security Risk
Understand, Assess & Manage Risk
Demonstrate that effective governance, policies and processes are in place to identify, assess and systematically manage cyber security risks across your organisation, systems, data and supply chain.
Governance, risk management, assets and supply-chain dependencies.
Protecting Against Cyber Attack
Prevent & Protect
Implement proportionate technical and organisational security measures to protect the networks and information systems supporting your essential business functions from cyber attack.
Preventative controls protecting systems, networks and data.
Detecting Cyber Security Events
Monitor & Detect
Maintain effective monitoring and detection capabilities to identify cyber security events that affect, or could affect, your organisation’s functions, systems and data.
Monitoring, logging, alerting and detection.
Minimising Cyber Incident Impact
Respond, Recover & Restore
Maintain effective incident response, recovery and resilience capabilities to minimise disruption and restore essential functions and data following a cyber security incident.
Incident response, recovery, continuity and restoration.
DCC Level 2 - Four Core Assessment Objectives
Managing Security Risk
Governance, risk management, assets and supply-chain dependencies.
Demonstrate that effective governance, policies and processes are in place to identify, assess and systematically manage cyber security risks across your organisation, systems, data and supply chain.
Protecting Against Cyber Attack
Preventative controls protecting systems, networks and data.
Implement proportionate technical and organisational security measures to protect the networks and information systems supporting your essential business functions from cyber attack.
Detecting Cyber Security Events
Monitoring, logging, alerting and detection.
Maintain effective monitoring and detection capabilities to identify cyber security events that affect, or could affect, your organisation’s functions, systems and data.
Minimising Cyber Incident Impact
Protecting Against Cyber Attack
Maintain effective incident response, recovery and resilience capabilities to minimise disruption and restore essential functions and data following a cyber security incident.
Cyber Essentials Plus is a prerequisite for DCC Level 3 and must remain current throughout the period of certification.
The Cyber Essentials Plus scope must appropriately align with the DCC scope. All business units included within the DCC scope must be covered by Cyber Essentials Plus for the systems and networks to which the Cyber Essentials scheme applies. DCC may extend further, including systems that fall outside normal Cyber Essentials scoping rules.
As a Cyber Essentials Certification Body, KEYSIGMA can coordinate your Cyber Essentials Plus and DCC scoping from the outset, helping ensure the certifications align properly, reducing duplication and providing a smoother, more efficient assessment process.
Getting the scope right is a critical part of DCC certification. Your scope should include the systems, services and business functions needed for your organisation to operate securely and resiliently. Defining this correctly at the outset helps avoid gaps, delays and the need to revisit the assessment later, and is crucial to ensuring your DCC certificate is suitable for, and accepted against, the MOD contracts your organisation is bidding for.
As part of the assessment, your KEYSIGMA Assessor will review the proposed scope thoroughly to confirm it is appropriate and sufficiently covers the organisation being certified.
Getting the scope right is a critical part of DCC certification. Your scope should include the systems, services and business functions needed for your organisation to operate securely and resiliently. Defining this correctly at the outset helps avoid gaps, delays and the need to revisit the assessment later, and is crucial to ensuring your DCC certificate is suitable for, and accepted against, the MOD contracts your organisation is bidding for. As part of the assessment, your KEYSIGMA Assessor will review the proposed scope thoroughly to confirm it is appropriate and sufficiently covers the organisation being certified.
Level 2 requires a minimum score of 80% within each assessment objective, with every control at least partially met.
DCC Level 2 is independently assessed by a qualified DCC Assessor against Def Stan 05-138 Issue 4. It is an evidence-based assessment covering 139 controls: your organisation must explain how each applicable control is met and provide evidence demonstrating that the required measures are implemented and operating effectively.
Controls are scored individually as Not Met, Partially Met or Fully Met. To achieve Level 2, your organisation must achieve at least 80% of the total points available within each of the four assessment objectives. Importantly, every control within each objective must also be at least partially met, a control scored as Not Met will cause that objective to fail, even where the overall points score reaches 80%. Both conditions must therefore be satisfied.
1. Theoretical Assessment
Your Assessor reviews your completed assessment responses, explanations and supporting evidence to determine how the applicable DCC Level 2 controls are being met.
Where evidence is incomplete or further context is required, the Assessor may request clarification or additional information before progressing to the Practical Assessment.
2. Practical Assessment
The Practical Assessment verifies that the controls described during the theoretical phase are implemented and operating effectively within the agreed DCC Level 2 scope.
The Assessor may review systems, configurations, records and supporting evidence, observe operational processes, speak with relevant personnel and control owners, and carry out appropriate sampling or walkthroughs to confirm that the required controls are working in practice.
3. Certification
Once the applicable DCC Level 2 requirements have been successfully demonstrated, KEYSIGMA, as an authorised DCC Certification Body, can issue your DCC Level 2 certificate.
DCC certification is valid for three years, subject to continued compliance with the applicable controls, maintaining the required Cyber Essentials Plus certification, and completing an annual attestation confirming that the certification scope has not changed significantly.
To protect the integrity of the scheme, DCC rules allow Certification Bodies to provide advice and identify gaps, but they cannot implement controls or carry out work that they will later assess.
To give you flexibility, KEYSIGMA offers two clear routes:
✔ Implementation Support – We can help you understand the requirements, identify gaps and implement the controls needed to meet the DCC standard. Your assessment would then be carried out independently by a trusted partner Certification Body.
✔ Independent Certification – If your organisation is ready for assessment, KEYSIGMA can independently assess you against the DCC requirements and, where successful, issue your certification.
Whether you need implementation support, independent certification, or both, KEYSIGMA can ensure the right expertise is in place while maintaining the impartiality required by the scheme.
Support or Certification
Keeping the Assessment Independent
To protect the integrity of the scheme, DCC rules allow Certification Bodies to provide advice and identify gaps, but they cannot implement controls or carry out work that they will later assess.
To give you flexibility, KEYSIGMA offers two clear routes:
✔ Implementation Support – We can help you understand the requirements, identify gaps and implement the controls needed to meet the DCC standard. Your assessment would then be carried out independently by a trusted partner Certification Body.
✔ Independent Certification – If your organisation is ready for assessment, KEYSIGMA can independently assess you against the DCC requirements and, where successful, issue your certification.
Whether you need implementation support, independent certification, or both, KEYSIGMA can ensure the right expertise is in place while maintaining the impartiality required by the scheme.